AI Governance
Validate Once Is Not Enough: Continual Learning, NIST, and ISO 42001.
By John Utley
Published
A launch review is still necessary. It is no longer sufficient if prompts, memory, retrieval sources, or weights can change once the system is in use. We validated it in October does not answer which version made this call in November.
NIST AI RMF already points at this through Measure and Manage: monitor performance, track incidents, and keep the system inside its intended use. ISO 42001 asks for monitoring and continual improvement, not a binder that is finished at go-live. The EU AI Act, where it applies, likewise assumes ongoing obligations, not a single classification event.
What to install now, with current tools:
- Layered memory, so working context is not mixed with approved policy.
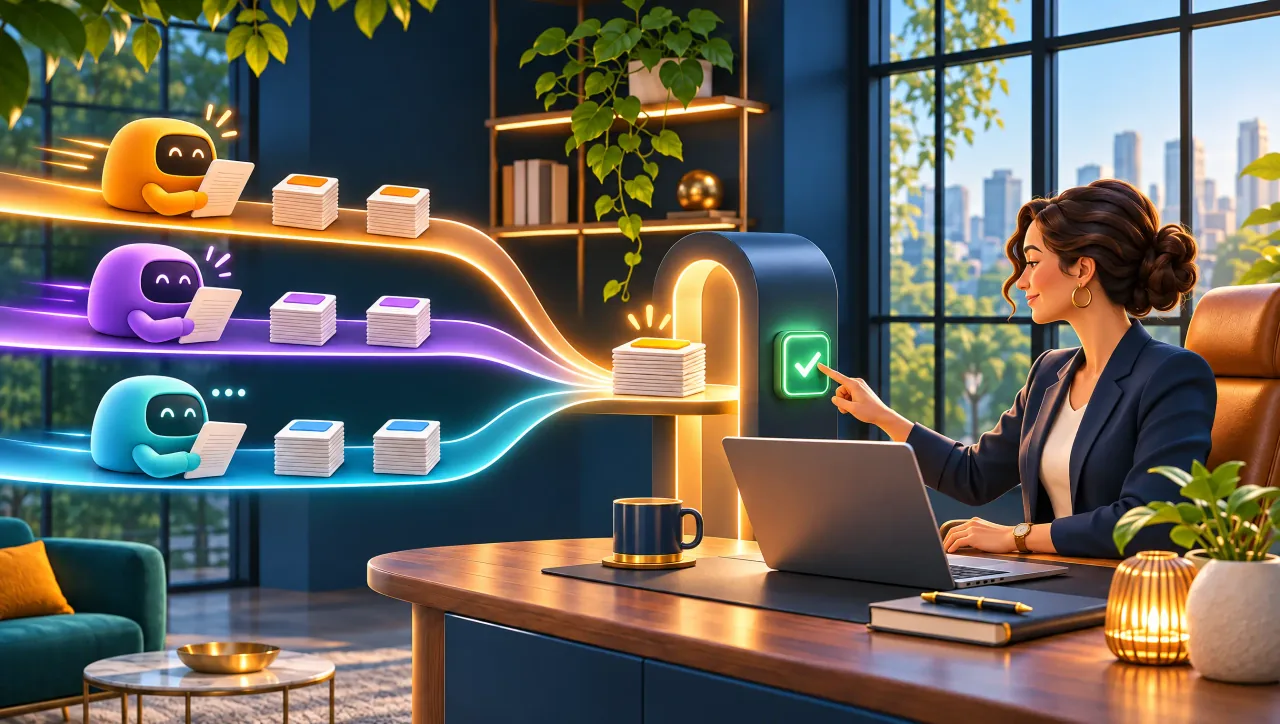
- A human promotion gate, so a lesson cannot become slow-layer policy without review.
- Combined versioning of model and memory, plus logs that record what was retrieved.
- Named write rights and a tested rollback for long-term memory.
- Written re-validation triggers: a changed retrieval source, a new use case, a material error rate, or a change to who can approve lessons.
Sophizo's Governance Accelerator stays a 90-day program inside its published scope, and these monitoring and memory-versioning practices belong in that program.
Teams that need a leadership stance first can request the 60-minute briefing, Governing AI That Keeps Learning. Teams that need a map of current learning surfaces can start with the Learning-Loop Audit.